Three Indian-Origin Researchers Use Claude AI to Breach OpenAI Systems and Win Bounty
World Pulse Editorial — The WORLD PULSE editorial team covers international news, business, technology, AI, science, sport, culture and other subjects of public interest. The desk applies source attribution, editorial checks, context and corrections standards across the publication.
The byline identifies the newsroom author or editorial team responsible for this publication. Where the story is based on external reporting, those sources are identified below.
AI-assisted production may have been used in the drafting workflow. Source verification, attribution and editorial review remain the responsibility of WORLD PULSE.
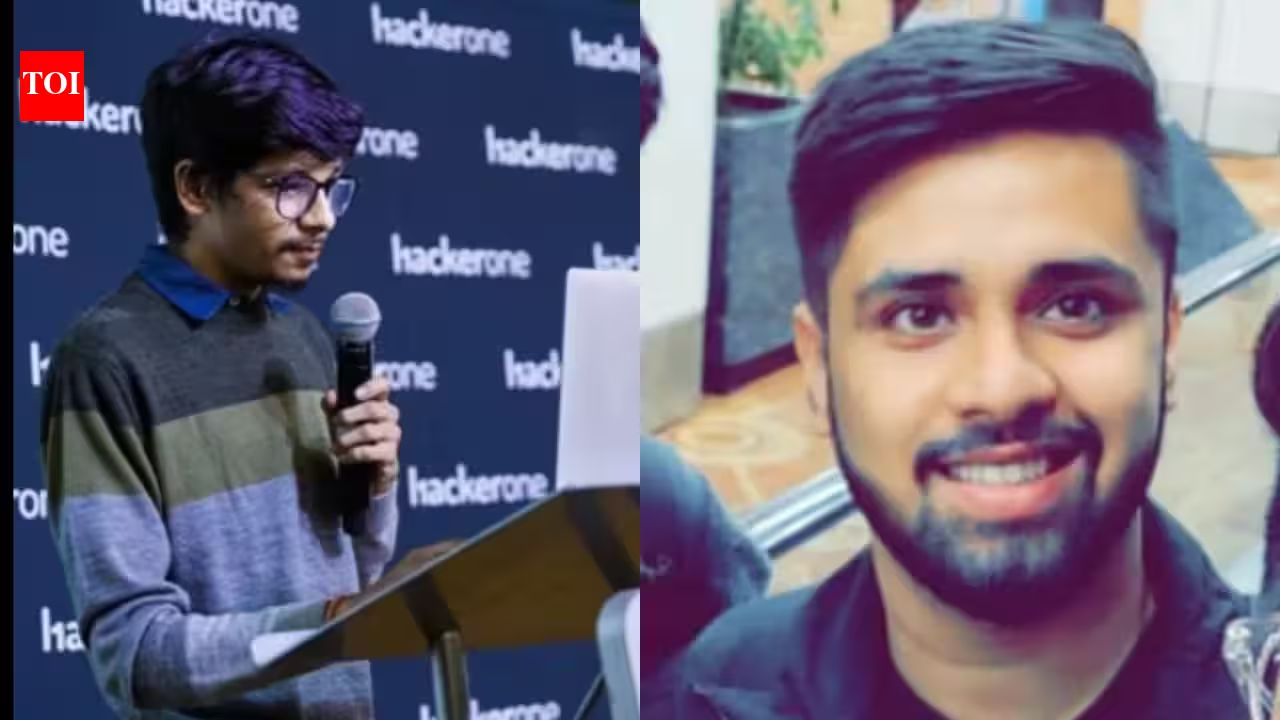
Three cybersecurity researchers of Indian origin demonstrated how Anthropic's Claude AI could be used to exploit vulnerabilities and access OpenAI accounts, securing a $6,500 bounty.
Three Indian-origin cybersecurity researchers, Harsh Jaiswal, Mohan Pedhapati, and Rahul Maini, demonstrated how Anthropic's Claude AI could be used to exploit vulnerabilities and gain access to OpenAI employee accounts alongside the company's internal code repository, according to reports. The security professionals, who are employed at the cybersecurity startup Hacktron AI, conducted their investigation in July while looking into security weaknesses across prominent artificial intelligence companies.
The research team chained two separate vulnerabilities to progress from OpenAI's public community forum to employee ChatGPT and Codex accounts, and subsequently into an internal GitHub repository. According to the researchers, the entire chain of events—from the initial discovery to demonstrating access to the internal repository—was completed in less than 72 hours. Furthermore, they spent under $3,000 on AI tokens during the operation and ultimately secured a $6,500 bounty after disclosing the issues to OpenAI.
The security breach originated at community.openai.com, the official OpenAI community and help forum operated on the third-party Discourse platform. Hacktron researchers found that specially crafted HEIC and HEIF image files could exploit a vulnerability within the image-processing software utilized by Discourse. This vulnerability was connected to the `libheif` image-decoding library and could potentially permit remote code execution, granting an attacker command-line access to the affected server.
Controlling the forum server by itself did not provide immediate entry into OpenAI's internal code. To safely demonstrate proof of access without viewing sensitive intellectual property or source code, the researchers utilized a compromised employee's Codex account to submit a harmless pull request to OpenAI's internal private repository. They prominently integrated Anthropic's Claude AI models, spending less than $3,000 in API tokens, to assist in writing, debugging, and porting binary exploits more rapidly. This demonstrated how offensive artificial intelligence capabilities can accelerate vulnerability research.
Following the tests, the findings were reported responsibly to OpenAI and Discourse through the Bugcrowd and HackerOne platforms. OpenAI patched the identity issue shortly after receiving the notification and awarded the team a $6,500 bug bounty. In a statement provided to Forbes, OpenAI spokesperson Drew Pusateri thanked the researchers for contacting the organization and sharing their findings, confirming that the vulnerability had been successfully resolved.
Tech commentator Deedy Das highlighted that the three researchers achieved this feat without traditional backing from prominent elite educational institutions or major technology corporations. Noting their backgrounds on LinkedIn, Das emphasized that the breakthrough was driven purely by raw curiosity and technical skill, illustrating that independent researchers can accomplish significant feats in modern cybersecurity.
The rapid execution and efficiency of the attack underscore the evolving role of generative artificial intelligence models in vulnerability research. By leveraging advanced language models to streamline exploit development, security analysts are able to uncover complex threat chains faster than ever before. Collaborative bug bounty programs continue to serve as a vital mechanism for major technology companies to identify and remediate such vulnerabilities before malicious actors can exploit them in the wild.
Topic coverage
Follow recurring subjects across the WORLD PULSE newsroom.
Topics
Reader interest
Most read
 UKKelsey Parker Welcomes New Baby Named River Following Heartbreaking Stillbirth
 AIOpenAI Discloses New Safety Issues and Outlines Plan for Tracking Incidents
 SportsAsian Games Facing Accommodation Crisis and Weather Disruptions in Nagoya, Japan
More from the newsroom
Latest stories
 UKUK Defence Secretary Wes Streeting Urges Public Preparation for Cyber, Climate and Supply Chain Emergencies
 USAFederal Charges Filed Against Virginia State Senator L. Louise Lucas in Alleged Racketeering Scheme
 WorldRising Islamophobia and the Democratic Response to Attacks on Muslim Candidates
 ScienceGlobal Biodiversity Fund Faces Criticism as Pharmaceutical Contributions Stagnate at $7,000
 TechnologyMemphis City Council Rejects One-Year Data Center Moratorium in Favor of 135-Day Halt
 WorldDiplomatic and Military Developments in the Middle East: Iran, Russia, and Regional Security Updates
 WorldRubio Denounces Ukraine’s Claims of Withdrawn U.S. Support as ‘Scandalous’ Amid Oslo Diplomacy
 USATrump Administration Proposes Tying Federal Transit Funding to Local Birth and Marriage Rates
Research & context
Explore WORLD PULSE reference pages
Use these newsroom indexes to follow related coverage, review publication timelines and explore how WORLD PULSE reporting is organized.
Sources & attribution
The external reports, announcements or publications used to inform this article are listed here for attribution and reader context. A source link does not mean WORLD PULSE independently endorses every claim in that source.
Questions about sourcing, attribution or corrections: contact the newsroom.